Introduction 🤖🔐
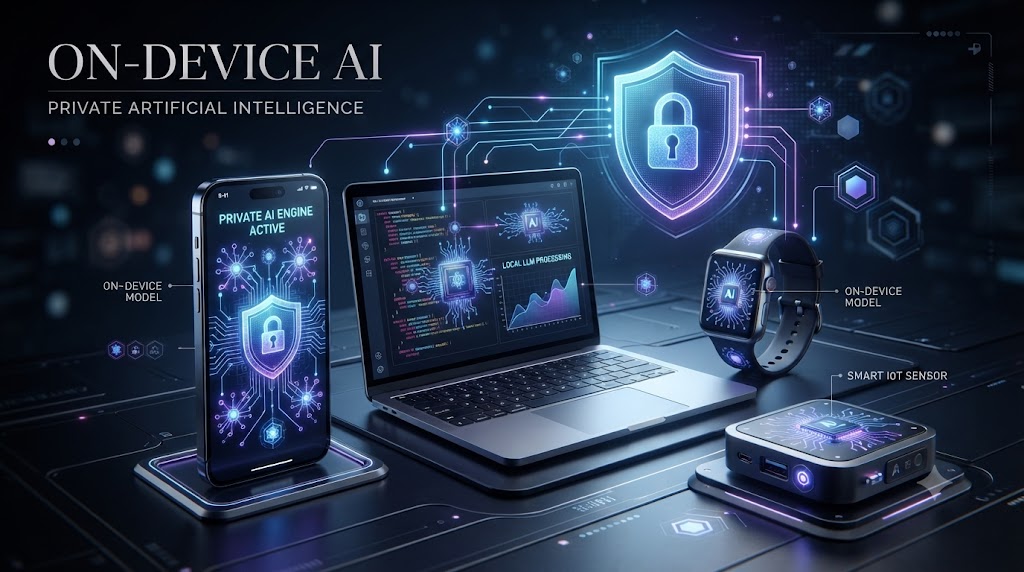
Artificial intelligence is entering a new phase in which intelligence does not always have to live in the cloud. On-device AI, sometimes called edge AI, enables AI models to run directly on smartphones, laptops, vehicles, wearables, industrial equipment, and other connected devices. At the same time, Private AI is developing around a broader objective: allowing AI systems to process sensitive information while reducing unnecessary exposure of that information to centralized servers.
Recent 2026 research shows that smaller language models, model compression, federated learning, privacy-enhancing technologies, and specialized hardware are making local AI increasingly practical. A September 2026 survey of more than 160 papers on small language models for IoT found that smaller models can provide advantages in privacy, latency, energy efficiency, and offline operation, particularly for specialized tasks.
This research direction could fundamentally change how personal and enterprise AI systems are designed.


7
What Is On-Device AI?
On-device AI refers to artificial intelligence inference performed directly on the hardware where data is generated or consumed. Instead of sending every voice command, image, sensor reading, or document to a remote data center, an AI model can process at least some of that information locally.
A smartphone, for example, can use an integrated neural-processing accelerator to perform speech recognition, image analysis, translation, text summarization, or other AI tasks without continuously communicating with a cloud service.
This architecture has several potential benefits. Local processing can reduce network latency, improve functionality when connectivity is poor, and reduce the amount of sensitive information that must leave the device.
Research published in 2026 increasingly treats these characteristics not simply as engineering conveniences but as important requirements for future AI systems. IEEE research on on-device small language models highlights low latency, privacy-preserving inference, energy efficiency, and the ability to operate without constant cloud connectivity.
Why Small AI Models Are Becoming Important 🧠
One of the biggest developments behind on-device AI is the improvement of Small Language Models (SLMs).
Large language models can require substantial memory and computational resources. This makes completely local execution difficult on many consumer and IoT devices. Smaller models are designed to perform specific tasks using considerably fewer resources.
A 2026 systematic review examined 68 studies involving small language models and found that techniques such as parameter-efficient fine-tuning can substantially reduce the computational requirements of adapting models.
Another 2026 survey specifically examining IoT applications describes SLMs below 7 billion parameters as a practical direction for resource-constrained environments. The researchers found that models in this category can provide competitive performance for classification and narrower tasks while offering benefits for privacy, latency, energy consumption, and offline operation.
The important change is that researchers are increasingly designing models for the device, rather than simply trying to shrink cloud models enough to fit onto devices.
Quantization, Pruning and Knowledge Distillation ⚙️
Making AI local requires more than simply selecting a smaller model.
Researchers are using several optimization techniques. Quantization reduces the numerical precision used to represent model parameters. Instead of storing calculations in high-precision formats, models can use lower-precision representations, reducing memory and computational requirements.
Pruning removes parameters or computational components that contribute relatively little to model performance. Knowledge distillation allows a smaller model to learn useful behavior from a larger teacher model.
These techniques can be combined with hardware-aware optimization so that models operate efficiently on specific processors.
The 2026 IEEE survey literature identifies compression, pruning, quantization, distillation, parameter-efficient adaptation, and inference optimization as central components of modern on-device SLM research.
Private AI: More Than Just Local AI 🔒
Private AI is related to on-device AI but is broader.
Running a model locally can reduce data exposure, but privacy does not automatically follow from local execution. Applications still need to protect stored information, model inputs and outputs, authentication credentials, model updates, and communications with external services.
This is why researchers are combining local inference with additional privacy and security technologies.
One important direction is federated learning. Instead of collecting all training data in a central location, devices can train models locally and send model updates for aggregation.
However, federated learning is not automatically private. Researchers have demonstrated that model updates can potentially leak information, which has created interest in techniques such as differential privacy and encryption. A 2026 study of resource-constrained devices, for example, investigated privacy-preserving federated transfer learning using fully homomorphic encryption.
Federated Learning for Private Intelligence
Federated learning could become an important component of private AI ecosystems.
Imagine thousands of smartphones learning from local user interactions without transferring raw personal data to a central server. The devices could train or fine-tune models locally, while a central system aggregates carefully protected updates.
Recent research is moving toward more sophisticated versions of this architecture.
A 2026 study on edge computing proposed adaptive privacy mechanisms that dynamically adjust privacy protection according to data characteristics and privacy requirements. The research addresses an important problem: stronger privacy mechanisms can sometimes reduce model utility, creating a trade-off between privacy and performance.
This means future private AI may not use a single privacy setting. Instead, systems could dynamically determine how much information can safely participate in collaborative learning.
The Rise of Hybrid AI ☁️📱
The future is unlikely to be exclusively cloud-based or exclusively device-based.
Instead, research increasingly points toward hybrid AI architectures.
A device may perform simple or sensitive operations locally while sending more computationally demanding tasks to a secure server. A private assistant could, for example, process personal information on the device and use a remote model only when a task requires capabilities unavailable locally.
Research into federated split learning follows a similar idea. A model can be divided between device and server, allowing resource-constrained hardware to perform part of the computation while more powerful infrastructure performs the rest. Recent research on FedSplitX specifically addresses heterogeneous devices with different computational capabilities.
This approach could become especially useful for organizations deploying AI across large fleets of devices with different hardware specifications.
Private AI and Long-Term AI Memory
One of the most interesting developments is the connection between private AI and AI memory.
Future assistants are expected to remember preferences, previous interactions, documents, schedules, and other contextual information. But long-term memory also creates significant privacy challenges.
In September 2026, Google DeepMind described an architecture for Private AI Compute intended to provide persistent, cross-device AI memory while maintaining privacy standards associated with on-device processing. The approach attempts to address the challenge of providing continuity across devices without simply exposing personal information to conventional cloud infrastructure.
This represents an important research question: Can AI remember more without knowing more than necessary about the person using it?
That question could shape the next generation of personal assistants.
On-Device AI in Healthcare 🏥
Healthcare is one area where private AI could have significant applications because medical information is highly sensitive.
AI running directly on medical devices could analyze physiological signals, images, or sensor data without continuously transferring raw information to a remote server.
Recent research illustrates this direction. A 2026 Scientific Reports study introduced HybridTrust, an on-device federated TinyML framework designed for medical IoT environments. The study explored secure collaboration among medical devices while addressing compatibility between existing and post-quantum cryptographic systems.
Potential applications include continuous monitoring, anomaly detection, wearable health devices, hospital equipment, and privacy-conscious clinical analytics.
However, healthcare AI also demonstrates why privacy alone is not sufficient. Models must be accurate, reliable, secure, explainable where appropriate, and carefully validated before being used in high-stakes environments.
Private AI and Cybersecurity 🛡️
As AI becomes more personal and autonomous, protecting the computation itself becomes increasingly important.
Confidential computing is one technology being investigated for protecting sensitive workloads even when computation occurs outside a user’s local device.
NIST’s 2026 draft report on hardware-enabled security describes confidential computing as a method for protecting data while it is being processed and discusses applications to AI workloads in cloud environments.
This creates another layer in the private AI architecture:
Device privacy → secure communication → protected computation → controlled storage
Rather than relying on one security mechanism, future systems may combine several.
The Energy Challenge ⚡
Local AI has an important advantage: it can reduce communication with remote servers.
But running AI models directly on a device consumes energy. This matters particularly for smartphones, watches, earbuds, sensors, drones, and battery-powered IoT systems.
Researchers are therefore examining energy-aware model architectures and hardware optimization. The goal is not simply to make a model smaller but to maximize useful AI computation for every unit of energy consumed.
Future AI benchmarks may increasingly measure:
- inference latency,
- memory requirements,
- energy per inference,
- thermal impact,
- privacy protection,
- accuracy,
- offline capability,
- and hardware compatibility.
This represents a shift away from evaluating AI purely by benchmark accuracy.
The Hardware–Software Connection
On-device AI depends heavily on specialized hardware.
Modern devices increasingly contain dedicated neural processing units or AI accelerators designed to perform machine-learning operations efficiently.
The relationship between model architecture and hardware is becoming increasingly important. Researchers are exploring hardware-aware neural-network design, operator fusion, adaptive model scaling, and specialized inference runtimes.
This could eventually produce AI models specifically optimized for particular categories of processors rather than general-purpose cloud infrastructure.
Challenges That Remain
Despite rapid progress, on-device AI still faces significant challenges.
The first is model capability. A smaller model may be excellent for a focused task but may not match the reasoning, knowledge, or multimodal capabilities of the largest cloud models.
The second is hardware fragmentation. Different phones, computers, vehicles, sensors, and embedded devices have different processors, memory capacities, and acceleration technologies. Researchers therefore need better standardized benchmarks and deployment tools. IEEE research identifies hardware fragmentation and reliable evaluation as important open challenges.
The third challenge is security. Local computation can reduce some privacy risks, but compromised devices, malicious applications, model extraction, adversarial attacks, and data leakage remain possible.
Finally, there is the problem of privacy leakage during collaborative learning. Federated learning reduces the need to transfer raw data, but model updates can still create security and privacy risks. This is why differential privacy, encryption, secure aggregation, and related technologies remain active research areas.
What the Future Could Look Like 🌐
The emerging research suggests that future AI will probably consist of multiple layers rather than a single giant model.
A smartphone might contain several specialized models: one for speech, another for vision, another for personal information retrieval, and another for lightweight reasoning. More demanding requests could be routed to a private cloud system.
Wearables could process health signals locally. Vehicles could analyze sensor information at the edge. Industrial equipment could detect failures without sending every sensor reading to an external data center.
Personal AI assistants could maintain private local memories while selectively synchronizing protected information across devices.
In this architecture, the cloud becomes a powerful partner rather than the location of every AI computation.
Conclusion
New research on on-device AI and Private Artificial Intelligence is moving the industry toward a more distributed model of computing. Smaller language models, quantization, pruning, federated learning, privacy-enhancing technologies, specialized AI hardware, and confidential computing are converging to make local and privacy-conscious AI increasingly practical.
The most important development may not be a single new model. Instead, it is the emergence of an AI architecture in which intelligence, privacy, hardware, and computation are designed together.
As AI becomes more deeply integrated into phones, healthcare systems, vehicles, workplaces, homes, and industrial environments, the ability to decide where computation occurs and who can access the underlying data will become just as important as model intelligence itself.
The next generation of AI may therefore be not only more capable, but also more local, more efficient, and more privacy-aware.